The European Union's Cyber Resilience Act reached an important operational date on 11 September 2026. Manufacturers must now report actively exploited vulnerabilities and severe incidents affecting the security of products with digital elements. For a Wi-Fi digital display-frame programme, the difficult question is rarely whether the product contains software. It is whether the brand, hardware assembler, firmware developer, mobile-app provider and cloud operator can identify the same product and move verified information to the responsible manufacturer quickly enough.
This guide is for EU importers, private-label brands, retailers, connected-frame product teams and OEM/ODM suppliers. It focuses on the Article 14 reporting workflow that now applies. The CRA's main product obligations apply from 11 December 2027, while the reporting obligations have an earlier application date and can reach products already made available on the Union market. This article does not determine the legal manufacturer, decide whether a vulnerability is actively exploited, classify an incident as severe or replace ENISA, CSIRT, legal or cybersecurity advice.
Start with the date that actually changed
The Commission states that CRA reporting obligations apply from 11 September 2026. The main obligations on product design, conformity, technical documentation and vulnerability handling apply from 11 December 2027. Buyers should keep those dates in separate rows of the launch plan. Saying that “the CRA starts in 2027” can cause a team to miss a reporting process that is already required; saying “all CRA obligations are active now” is equally inaccurate.
Create a dated scope note for every connected-frame family. Record which units are already on the EU market, which remain in production and which new models are planned for 2027. The Commission's legislative summary says reporting applies to products with digital elements already made available on the Union market, including products placed on the market before the main application date. Ask qualified counsel to confirm how this applies to the actual distribution history.
Confirm that the product is more than a decorative frame
A traditional passive frame does not become a connected product because a buyer discusses it online. A digital frame may include an operating system, Wi-Fi or Bluetooth radio, mobile application, remote content service, update client, media decoder, local storage and third-party libraries. Map the real architecture rather than relying on the merchandising name “smart frame.”
Draw a simple system boundary: physical frame, display controller, radio module, firmware, operating system, mobile app, API, cloud storage, administrator portal and update service. Note which functions are part of the product, which are remote data-processing solutions and which are third-party services outside the supplier's control. A lawyer and cybersecurity specialist should validate the CRA scope; the factory should provide technical facts, not issue an unsupported legal conclusion.
Identify the manufacturer before an incident occurs
Private-label arrangements can blur roles. The factory may assemble a reference platform, a software vendor may supply the app, and the EU brand may sell the finished model under its own name. CRA duties follow legal definitions and facts, not the party described casually as “the supplier.” The commercial contract should name who performs each operational task without pretending that a contract can rewrite statutory responsibility.
Create a responsibility map covering the manufacturer, importer, distributor, authorised representative if appointed, software providers and security-response contacts. Include legal entity names, establishment countries, twenty-four-hour escalation routes and deputies. If the business cannot identify the reporting owner during an ordinary launch review, it will not find that owner reliably during a weekend vulnerability event.
Build one controlled product identity
A report about “the ten-inch Wi-Fi frame” is not actionable when several models share an enclosure. Assign a commercial model, hardware revision, firmware build, operating-system image, radio-module identity, mobile-app version range, cloud environment and support status. Link the identifier visible to the user with the deeper configuration held by the technical team.
Keep a model genealogy showing which private labels and regional variants use the same platform. Record whether a change affects only packaging or changes code, credentials, radio behaviour, cryptographic components or update capability. Product identity should survive a retailer rename. Avoid putting personal data into serial formats, and do not assume a removable carton label will remain available after installation.
Make vulnerability intake reachable and owned
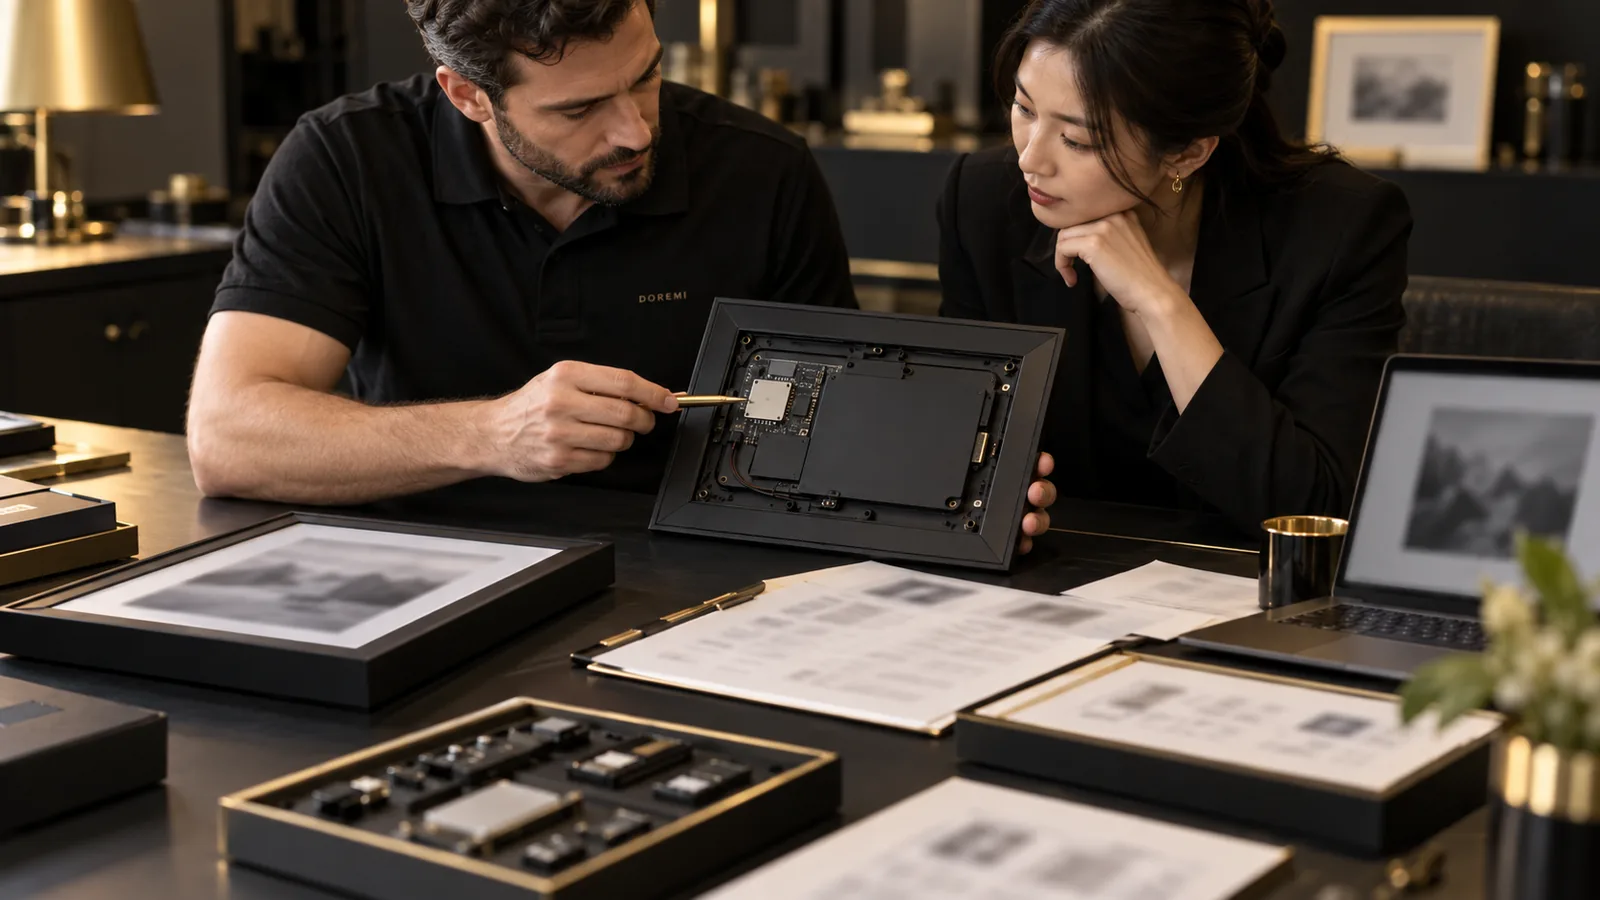
A security researcher, retailer, customer, app-store reviewer, supplier or employee may discover the first signal. Publish or otherwise maintain a monitored vulnerability-contact route appropriate to the product and organisation. Define the information requested without forcing a reporter to expose sensitive details publicly. A dormant mailbox is not a process.
Route incoming reports to a named product-security owner and backup. Preserve the original submission time, reporter contact preferences, affected version, reproduction details and any evidence of exploitation. Acknowledge receipt without promising a bounty, legal outcome or fix date that has not been approved. Give customer support a simple escalation trigger so a technical complaint is not closed as an ordinary pairing issue.
Separate a vulnerability from active exploitation
Not every bug is an actively exploited vulnerability, and not every service outage is a severe security incident. The reporting decision requires qualified assessment against the CRA and current guidance. Procurement should not make that decision, but it can ensure that the evidence and specialists are available.
Prepare an assessment record with the technical description, affected versions, exploit prerequisites, observed indicators, data or functions at risk, geographic distribution, known attacks, mitigation options and confidence level. Document what is known, unknown and being verified. Do not wait for perfect forensic certainty before escalating internally; the legal clock may run from awareness, so uncertain high-impact signals need immediate review.
Design the 24-hour and 72-hour path
The Commission describes an early warning within 24 hours of awareness and a fuller notification within 72 hours for the covered events. Those windows are not compatible with a chain in which the EU team emails a sales representative, who waits for the next factory workday, who then asks an unnamed firmware subcontractor. Set a direct emergency route across time zones.
Run a tabletop exercise with a realistic scenario: a researcher reports that an exposed service is being used to take control of frames. Ask who validates the model, who contacts legal and security leaders, who can access the CRA Single Reporting Platform, who approves the early warning and who continues the technical investigation. Measure the handoffs. The exercise should test retrieval and decision readiness, not manufacture a conclusion.
Use the Single Reporting Platform correctly
ENISA's CRA Single Reporting Platform became operational on 11 September 2026. The Commission says manufacturers submit the required notifications through that platform. Access, identity, internal approval and secure evidence handling should therefore be arranged before a reportable event, not improvised after an alert.
Record the authorised submitters and deputies, but never place credentials in the product brief or share them with an unrelated factory contact. Maintain a secure internal path for evidence and decision notes. A supplier may contribute technical facts, yet the authorised reporting owner should control what is submitted, when it is submitted and how later updates remain consistent with the initial warning.
Map the app and cloud dependencies
Many connected frames are sold as hardware but depend on a licensed application and cloud platform. The brand needs to know who controls accounts, authentication, encryption, content delivery, logs, updates, libraries, hosting regions and incident telemetry. “The app is third party” is not an adequate handover if the product cannot operate securely without it.
Request a dependency register with commercial and technical owners, version or service identity, notification commitments and end-of-support conditions. The register should distinguish a component supplier from the legal manufacturer and should be updated when vendors or services change. Contractual notification time should leave the responsible manufacturer enough time to assess and meet any legal reporting window.
Control software bills of materials without treating them as proof
A software bill of materials can help identify affected components, but possession of an SBOM does not prove that a product is secure or that every vulnerability is exploitable. Ask for a machine-readable or controlled component inventory appropriate to the development process, linked to a specific release and build method.
Define how open-source and commercial component alerts are monitored, who evaluates them and how results reach the frame product owner. Include bootloader, operating system, media libraries, wireless stack, app SDKs and update client where relevant. Protect sensitive build information and give access based on need. The useful outcome is traceability from an advisory to deployed models, not a decorative compliance file.
Protect the update mechanism itself
A connected frame needs a controlled way to receive security fixes. Ask how update packages are authenticated, how integrity is verified, whether rollback is possible, what happens during power loss and how the product handles an expired certificate or unavailable server. These questions require competent engineering review and testing.
Document who can sign and release firmware, separation of development and production keys, emergency approval, staged rollout, failure monitoring and customer communication. A retailer's desire for a branded startup screen must not result in uncontrolled firmware forks. Each supported build should remain linked to source, configuration, test evidence and a release owner.
Define a support period that procurement can fund
The CRA framework links vulnerability handling to a support period. A private-label price comparison is incomplete if one quote includes maintained software and another assumes the app platform will simply continue. Ask for the proposed support period, update service, monitoring responsibilities, hosting costs, component availability and exit plan.
Translate the plan into commercial milestones: security contact availability, critical-fix response, routine maintenance, app-store compatibility, cloud operation, certificate renewal, customer notices and end-of-support communication. Avoid promising “lifetime updates” without a defined product lifetime, scope and funding model. The EU team should validate required duration against the final CRA rules and actual product.
Handle substantial modifications as a release decision
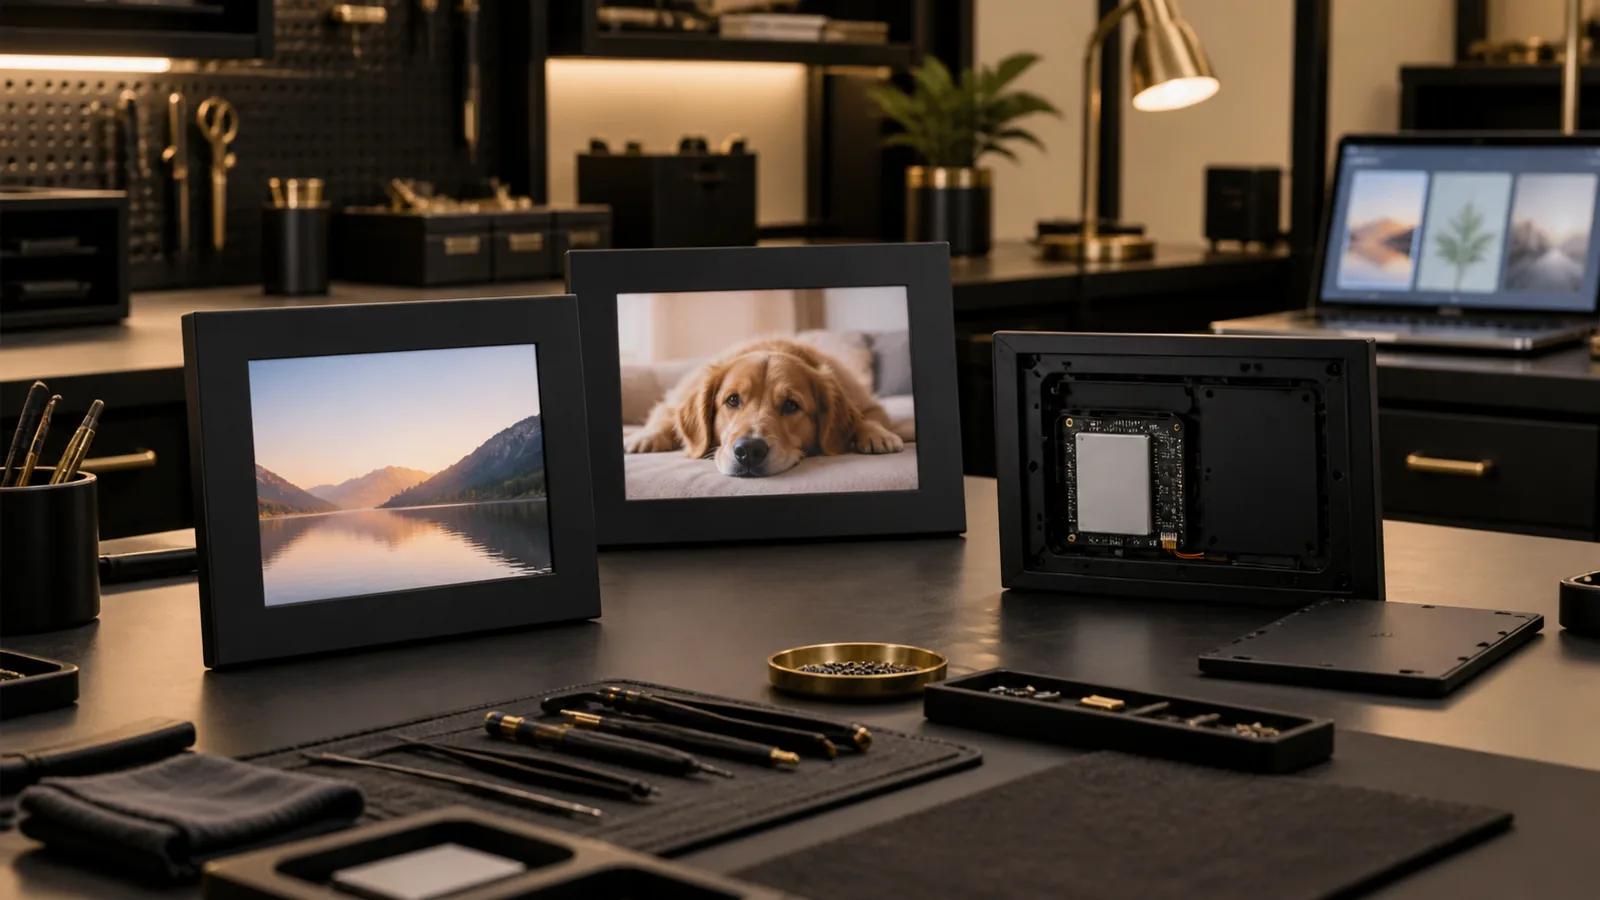
The Commission notes that products placed on the market before 11 December 2027 are generally subject to the main CRA obligations from that date if they undergo a substantial modification, while reporting already has broader application. A firmware feature, new cloud connection, radio-module substitution or private-label fork should trigger documented change assessment.
Use a release gate that asks whether the change affects intended purpose, cybersecurity risk, essential functions, conformity evidence, instructions, support or product identity. Qualified owners must decide the regulatory consequence. A supplier should never describe a change as “minor” simply because the enclosure and retail SKU remain visually unchanged.
Connect complaints, privacy and security without mixing conclusions
Unexpected account access, unknown images, repeated resets, disabled updates or unusual network traffic may be security signals. They may also have non-security causes. Preserve exact customer observations, timestamps, versions and consent for any diagnostic collection. Avoid requesting personal photographs when technical logs or identifiers are sufficient.
Route privacy questions to the privacy team and security incidents to the security team while keeping a shared chronology when necessary. CRA reporting does not replace GDPR, consumer safety, radio, electrical or contractual incident duties. The response owner should coordinate parallel obligations without assuming that one notification satisfies every regime.
Plan containment that does not destroy evidence
Possible actions may include blocking a vulnerable service, rotating credentials, pausing distribution, withdrawing a build, issuing an update or advising users. The correct action depends on verified facts and qualified risk assessment. Procurement's role is to make product population, channel inventory and supplier access visible.
Maintain the ability to freeze a firmware release, identify affected serial or batch ranges and contact distributors. Preserve representative devices, logs and software artifacts before wiping or reworking them. Do not publish exploit details casually, and do not promise that a factory reset resolves a vulnerability unless technical validation supports the instruction.
Require an OEM incident evidence pack
The supplier handover should include product architecture, model matrix, approved component lists, firmware and app identities, build and release owners, vulnerability contact, update method, dependency register, available logs, distribution quantities and change history. Add time-bound escalation commitments and a secure evidence-transfer route.
Test whether the pack can answer a specific question: “Which EU units contain this wireless library and which supported update can reach them?” If the answer requires several days of manual reconstruction, the evidence is not yet operational. Keep the pack current through purchase orders, engineering changes and software releases rather than rebuilding it during an incident.
Buyer release checklist
- Connected functions and remote dependencies are mapped
- Legal manufacturer, importer, distributor and reporting owner are identified
- Commercial model, hardware revision and software builds are linked
- Products already on the EU market are included in reporting readiness
- Vulnerability intake is monitored with a named backup
- Assessment can distinguish vulnerability, exploitation and severe incident signals
- Twenty-four-hour and seventy-two-hour escalation routes have been rehearsed
- Authorised Single Reporting Platform access is arranged
- App, cloud and component providers have fast notification commitments
- SBOM and release records connect advisories to deployed models
- Firmware updates are authenticated, testable and recoverable
- Support period and operating cost are commercially owned
- Changes trigger cybersecurity and regulatory review
- Containment preserves units, logs and release evidence
- Other privacy, product-safety and market duties remain separately assessed
Experience scope and project limits
Editorial review: Jessica, Founder & Project Advisor at DOREMI Display. Updated 13 September 2026. Jessica's practical scope covers B2B display-frame requirements, materials, samples, packaging, production coordination, quality discussions and supplier-to-buyer handover. She is not presented as ENISA, a CSIRT, an EU market-surveillance authority, a cybersecurity laboratory, legal counsel or the person who determines a CRA report.
This guide is educational preparation for connected-frame sourcing. It does not establish that a particular frame is in scope, that an event is reportable or that any described control satisfies the CRA. Product architecture, software, placing-on-the-market history and business roles require qualified, current review. Follow the official reporting process and seek urgent legal and cybersecurity advice when an actively exploited vulnerability or severe incident may exist.